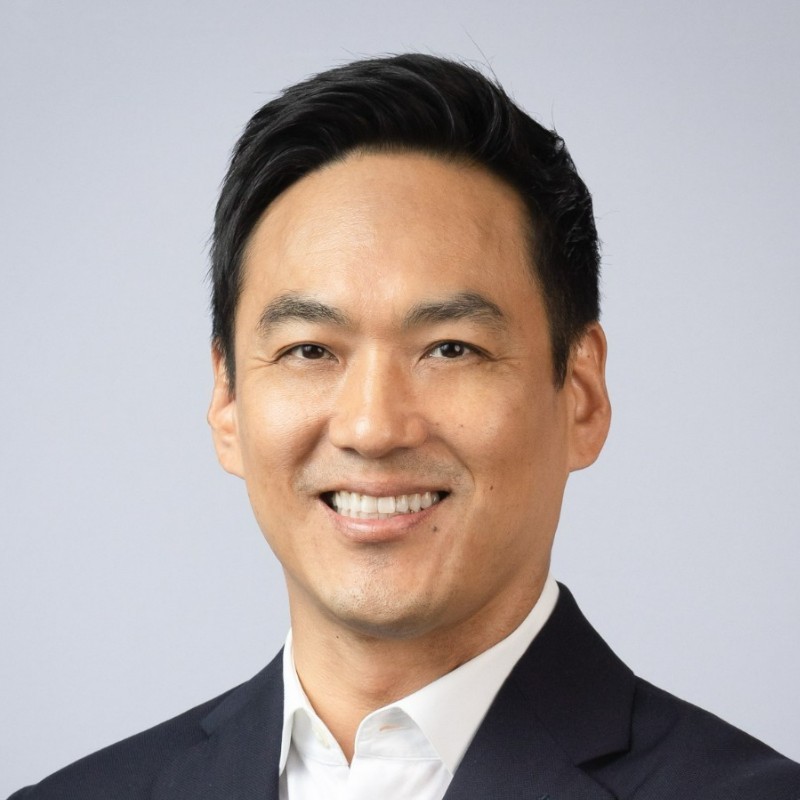
Greg Kim
VP & CISO at Sandisk | AI Security & Cyber Risk | 2025 ORBIE Global CISO of the Year
Inspire Leadership Network•Irvine, California, United States
View LinkedIn ProfileExecutive Overview
VP & Chief Information Security Officer at SanDisk. I lead global cybersecurity at a pivotal moment in compute history - protecting the intellectual property, infrastructure, and supply chains behind the advanced storage powering the world's AI. 25+ years of driving global cybersecurity and IT transformation across the semiconductor and technology sectors.CURRENT MANDATEPrimary security advisor to the Board of Directors and Audit Committee. Accountable for enterprise information security across manufacturing, design, and commercial operations in nine countries:- Cybersecurity strategy, architecture, and security operations- Identity and access management, Zero Trust, threat and vulnerability management- AI security: guardrails for AI agents and MCP integrations, and secure enterprise AI adoption- Cyber risk governance, regulatory compliance, and board-level reportingWHERE I'VE LED CHANGEAs VP, Global CISO and Interim CIO at Skyworks Solutions (S&P 500 semiconductor):- Built the enterprise security program from scratch. Earned ISO 27001 certification as one of the first among the top 30 global semiconductor companies, plus CMMC, TISAX Level 3, NIST CSF 2.0, GDPR, and CCPA- Led IT M&A integration for the $22B Qorvo acquisition, targeting $500M+ in annual cost synergies- Defended semiconductor R&D and proprietary IP against nation-state Advanced Persistent Threat and e-criminal campaigns with zero material business impact- Built the AI Governance, Security, and Enablement program: prioritized high-return use cases, set guardrails for AI agents and MCP integrations, and drove enterprise adoptionINDUSTRY ENGAGEMENTFounding Chapter Chair, SoCalCISO (Inspire Leadership Network) • Featured Speaker and Governing Body Member, Evanta Southern California • Contributor, SIA CISO Workgroup • Member, Defense Industrial Base Cyber Threat Sharing Initiative (U.S. DoD), OCIAC, and IT-ISACRECOGNITION & EDUCATION2025 SoCal ORBIE Global CISO of the Year • 2020 IDG CSO50 Award for Cybersecurity Transformation • CISSP • CCSK • Stanford Advanced Cybersecurity Professional Certificate (2026)
Career Timeline
- SandiskCurrentAug 2026–Present· 3 mos
- Vice President, Chief Information Security OfficerCurrentAug 2026–Present
- Inspire Leadership NetworkCurrentOct 2025–Present· 1 yr 1 mo
- Founding Chapter Chair | SoCalCISOCurrentOct 2025–Present
- Aug 2004–Jul 2026· 21 yrs 11 mos
- Chief Information Security Officer and Vice PresidentJul 2024–Present
- Chief Information Security OfficerAug 2019–Present
- Interim Chief Information Officer (CIO)Apr 2026–Jul 2026
- Vice President, Global CISO & IT OperationsJul 2024–Jul 2026
- Global CISO - Sr. DirectorApr 2020–Jun 2024
- Sr. Director, Cyber Security & ComplianceApr 2020–Jun 2024
- Director, IT Infrastructure and Cyber SecurityApr 2016–Apr 2020
- Manager, Information TechnologyAug 2004–Apr 2016
- Jul 2000–Aug 2004· 4 yrs 1 mo
- Principal SpecialistJul 2000–Aug 2004
Education
Advanced Cybersecurity Professional Certificate
Stanford University
Bachelor's degree
Economics
University of Minnesota